• About
  • Advertise with us
  • Privacy Policy
  • Contact Us
  • Home
  • CEO Stories
  • Industry Insider
    • AUTOMOBILE
    • Business
    • Education
    • Energy
    • Finance
    • Healthcare
    • Marketing
    • Law &Legal
  • Magazines
  • Women in Business
  • Blogs
  • Press Release
No Result
View All Result
  • Home
  • CEO Stories
  • Industry Insider
    • AUTOMOBILE
    • Business
    • Education
    • Energy
    • Finance
    • Healthcare
    • Marketing
    • Law &Legal
  • Magazines
  • Women in Business
  • Blogs
  • Press Release
No Result
View All Result

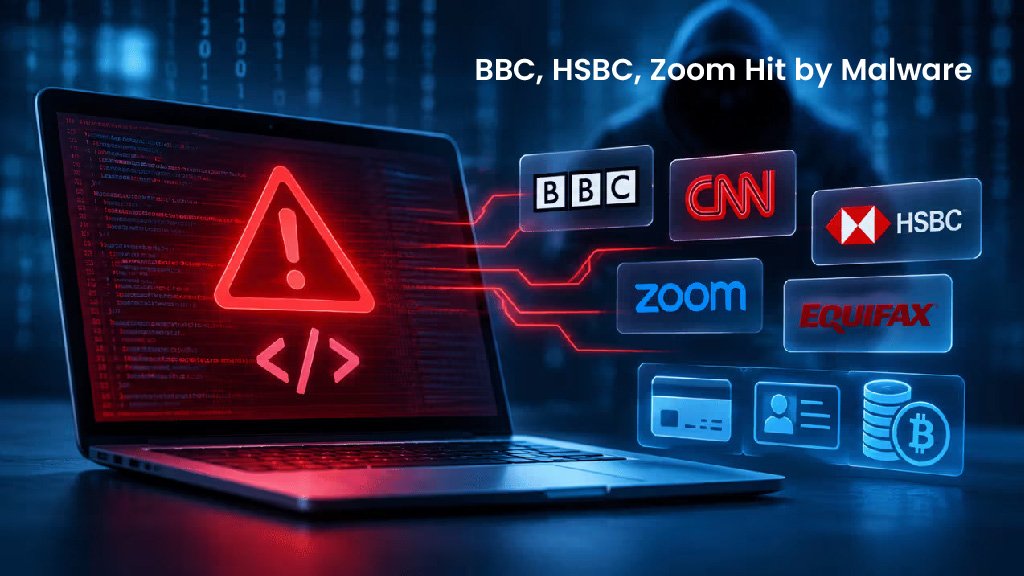
BBC, HSBC, Zoom Hit by Malware

by prime
Share on FacebookShare on Twitter

In the season of cyberattacks, another large-scale cyberattack has exposed thousands of users to malware after attackers compromised the Optimizely Web experimentation platform. According to Report URI, this incident has affected 178 organizations and used their trusted infrastructure to deliver malicious code to users. Researchers said that the attackers have injected malicious JavaScript into Optimizely customer projects, which eventually allowed malware to be served through websites that would be considered safe.

According to the investigation, 188 compromised JavaScript snippets belonging to 178 organisations were identified after researchers examined 1,611 Optimizely scripts. The affected organisations spanned sectors including banking, financial services, technology, retail, media, travel and healthcare.

Later, Optimizely also confirmed that an unauthorised party had exploited a vulnerability in its Experimentation account sign-up flow to add malicious JavaScript to certain customer projects. The company has blocked the vulnerable access route, deployed a fix, removed the injected code, terminated active sessions, and revoked access tokens. It also notified affected customers.

Experts say the malware was specifically designed to perform several malicious activities, including stealing cryptocurrencies, capturing card details, and taking screenshots. Attackers also deployed the Corouna and DarkSword iOS exploit kits to compromise iPhones and iPads. The script swapped cryptocurrency wallet addresses for the attackers and skimmed card details. By 19: 25 UTC, the attacker’s wallets had received around $7040.

While most of the malicious code was removed by Monday evening, URI advised anyone who visited the affected site on Monday to update their iPads and iPhones and also check for any unwanted crypto transfers and card statements for potential theft.

prime

Related Posts

Apple Unveils New Security Controls Amid Rising Risk from AI Agents

November 17, 2026

Microsoft’s Global Outage Deepens as Recovery Measures Fail to Restore Outlook, Teams and Copilot

November 16, 2026

Why Hospitality Real Estate Deserves a Place in Executive Investment Portfolios

November 12, 2026

Why High Performers Outsource Leisure Facility Care

November 12, 2026

How to Protect Corporate Brand Equity Across Digital Touchpoints

November 12, 2026

Why Customer Reviews Belong in the Operations Plan

November 6, 2026

Prime View Magazine showcase the wonderful stories of Founder’s, CEO’s, VP’s, Director’s and business and the unique services offered by them. Our website is one of the best online and digital platform for latest business news information.

Read More...

Our Services

  • Write For Us
  • Magazines
  • Press Release
  • Advertise with us

Company Info

  • Contact us
  • About Us
  • Terms & conditions
+1 334-846-5179
info@primeview.co

@2026 - All Right Reserved | Designed and Developed by Prime View.

No Result
View All Result
  • Home
  • CEO Stories
  • Industry Insider
    • AUTOMOBILE
    • Business
    • Education
    • Energy
    • Finance
    • Healthcare
    • Marketing
    • Law &Legal
  • Magazines
  • Women in Business
  • Blogs
  • Press Release

@2024 - All Right Reserved | Designed and Developed by Prime View.

Hi, how may I help you?

Exit mobile version